
Banking software must be reliable and understandable to guarantee unhindered access for all users. Therefore, the requirements for its testing are higher than for other types of programs or applications. In 2026, with mobile-first banking, open banking APIs, and increasingly sophisticated cyber-threats, that bar is higher than ever.
An online banking product must not only process transactions but also be secure and functional. Its testing can be a very long and laborious process. What options should you pay special attention to, and how should you proceed step by step during banking and fintech application testing? You will learn below.
Basic Requirements for Banking Applications
Image source: pexels.com
The functionality of banking software can vary depending on its purpose. However, most functions are similar. High-quality online banking should allow users to check account balances, make transactions, and pay for services or goods.
Here are some of the main requirements that banking software should meet:
- Work correctly and quickly. User data should be updated in real-time.
- Protect user information. An online banking application contains confidential data that must be kept safe from third-party access.
- Be resistant to hacker attacks. Many fraudsters may try to disclose financial information. Banking software should be ready to cope with this.
- Fintech app testing from time to time. This will prevent the emergence of all sorts of vulnerabilities and their harmful impact.
- Perform several operations simultaneously. The consumer should be able to make transfers and monitor the balance at the same time.
- Update quickly and on time. Any software needs constant improvement. Online banking should accept changes quickly so as not to interfere with the execution of user transactions.
High-quality banking software is a reliable, functional, and modern product that requires thorough testing before release and after each update.
Required Elements for Banking Software Testing
Image source: pexels.com
When testing banking products, most testers face difficulties in examining updates, fast and error-free data transfer, and program compatibility with different types of devices. To ensure the reliable operation of the product, QA engineers need to test all modules and elements of the program. In addition, they should consider the following:
- Compliance with regulatory requirements. Banking software has high certification and standardization requirements – from PSD2 and Open Banking standards to GDPR and PCI DSS. Their fulfillment is mandatory.
- Correctness and simplicity of transactions. Users should be able to make money transfers easily, correctly, and quickly.
- Ease of navigation and use. Since the program can be used by people of different ages and levels of experience, its interface should be intuitive. Each of them should be able to quickly understand the application or program.
- Quick reflection of changes. As soon as users make a transfer, it should be reflected in their balance. Changes should be almost simultaneous.
- Ability to work under overloads. Sometimes the load on the program may be greater than usual. It should not affect the speed and correctness of its performance.
- Absolute security and data confidentiality. Each software should have several phases of protection to ensure that no information is disclosed.
- Compatibility with different devices. Both the web program and the application should work smoothly on various gadgets, operating systems, or browsers.
Neglecting to test online banking functions comprehensively can lead to a decrease in product popularity and a deterioration in developer reputation.
Step-by-Step Banking Product Testing Plan
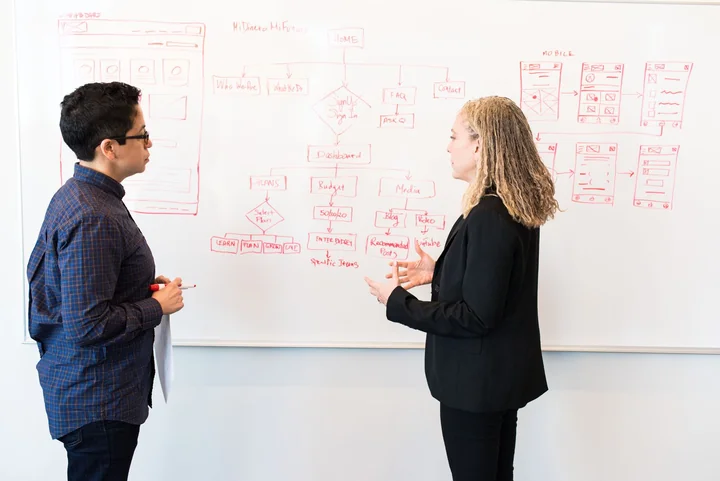
Image source: pexels.com
To ensure that you don’t miss any feature of your software, you need to have a clear plan. It will help ensure the highest reliability and security of the application. The following are the basic stages you have to go through.
Research Industry Requirements
Banking software has many features, so you need to familiarize yourself with similar products on the market to achieve success. In addition, take the time to study the regulatory documents.
Create a Detailed Testing Plan
You need to decide what you will test, what approaches and tools you will use, and what devices you will involve. You also need to make sure that you have enough resources to examine the product, or engage a third-party vendor to help.
Create Test Cases
They should have a wide range of coverage and provide thorough verification of the program or application. If you plan to implement an automated approach, consider making test cases reusable.
Perform Testing
You can prefer a manual approach or involve modern tools and automated tests. They can increase the product’s quality and help save you time and costs.
Cope with Retesting
Once all the bugs are fixed, you need to retest the product to make sure that no new errors have appeared in its operation.
Modern Trends Shaping Banking Software Testing in 2026
Image source: pexels.com
The way banks build and test software has changed rapidly. When planning your QA strategy today, it is worth accounting for the following trends:
- Security-first (DevSecOps): Security testing is no longer a final step. Static and dynamic analysis, dependency scanning, and penetration testing are built into the delivery pipeline so vulnerabilities are caught early.
- AI-assisted and automated testing: Machine-learning tools help generate test cases, spot flaky tests, and prioritise high-risk areas, while automation frameworks handle regression across releases.
- Open Banking and API testing: With third-party integrations and open APIs now central to banking, thorough contract and integration testing of those endpoints is essential.
- Fraud, biometric, and authentication testing: Multi-factor authentication, biometrics, and real-time fraud detection all need dedicated test coverage.
- Performance and resilience: Load, stress, and chaos testing confirm the product stays fast and available during peak demand and partial outages.
The UK Regulatory Layer Testing Has To Satisfy
Image source: pexels.com
In Britain, testing banking software is not only good engineering practice; it is part of how firms demonstrate they meet regulatory expectations. The FCA and the Prudential Regulation Authority require firms to identify their important business services, set impact tolerances for how much disruption is acceptable, and show they can stay within them in severe but plausible scenarios. Testing is how that is demonstrated: not only that features work, but that services recover, degrade gracefully and stay within tolerance when components fail.
Strong Customer Authentication
Image source: pexels.com
Payment journeys in the UK must meet strong customer authentication rules, which require two independent factors from something the customer knows, has or is. Testing has to cover not just the happy path but the exemptions, such as low-value and trusted-beneficiary rules, the fallbacks when a device or biometric fails, and the accessibility of the whole flow. Authentication is also where many customer complaints originate, so usability testing matters here as much as security testing.
Card Data And PCI DSS
Image source: pexels.com
Any system that stores, processes or transmits card data falls under the Payment Card Industry Data Security Standard. Version 4.0 of the standard became the only active version in 2024, with its remaining future-dated requirements becoming mandatory from March 2025, bringing stronger expectations around authentication, scripts on payment pages and targeted risk analysis. For testers the practical effects are regular vulnerability scanning, penetration testing of the cardholder data environment, and evidence that controls work as described.
Intelligence-Led Testing: CBEST
Image source: pexels.com
For the most systemically important firms, the Bank of England runs CBEST, a framework for intelligence-led penetration testing that simulates the tactics of real threat actors against live production systems. It goes well beyond a conventional penetration test, starting with a threat intelligence assessment tailored to the firm and ending with remediation plans reviewed by the regulator. Smaller firms are not in scope, but the approach, testing against realistic adversaries rather than a checklist, is the direction the whole industry is moving.
Test Data Without Real Customers
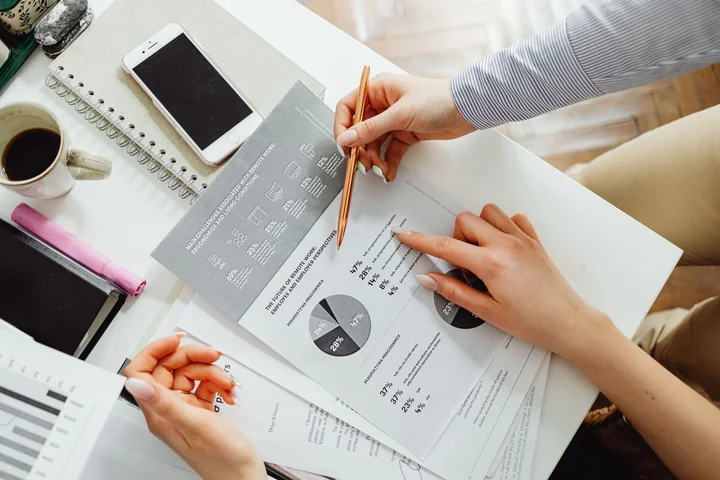
Image source: pexels.com
Banking tests need realistic data, and using real customer records in test environments creates serious data protection risk under UK GDPR. The established approaches are synthetic data generated to match the statistical shape of production, and properly masked or tokenised copies where production-like data is unavoidable. Test environments are also a common weak point for attackers precisely because they are less protected, so access controls and logging in test should be treated seriously rather than as an afterthought.
Accessibility Is A Requirement, Not A Nice-To-Have
Image source: pexels.com
Banking apps must be usable by customers with disabilities, and in the UK that is backed by equality law and by the FCA’s focus on consumer outcomes. Accessibility testing covers screen readers, keyboard-only navigation, colour contrast, text resizing and time limits, which frequently cause problems in authentication and payment steps. Automated tools catch a portion of issues; manual testing with assistive technology catches the rest. Building it into the test plan from the start is far cheaper than fixing it after release.
Performance And Peak Days
Image source: pexels.com
Banking systems face predictable peaks, payday, the end of the month, Black Friday and tax deadlines, and failures on those days are highly visible. Load and stress testing should model these peaks realistically, including third-party dependencies such as card schemes and payment networks, and verify that the system fails safely if limits are exceeded rather than corrupting transactions. Results should feed directly into capacity planning and into the firm’s operational resilience evidence.
Where To Read Next
Image source: pexels.com
For the broader decision about whether to build testing capability in-house or buy it in, see our guide to information technology outsourcing, and for how automated systems are coordinated and governed, our guide to AI orchestration. For the customer side of security, our guide to staying safe online covers two-factor authentication and passkeys.
FAQs
1. Why is testing banking software more demanding than other apps?
Because it handles money and highly confidential data, banking software must meet strict security, compliance, and reliability standards, leaving very little room for error.
2. What types of testing are most important for banking apps?
Security testing, functional testing, performance/load testing, compatibility testing, and regulatory-compliance checks are all critical.
3. How often should banking software be tested?
Continuously – before every release and after each update – ideally with automated tests running throughout the development pipeline.
For recovering data when things go wrong, see our guide to granular recovery technology.